


On 8 July 2026, the GPS card in a Telstra stratum-1 time server in Melbourne, Australia, reset and began sending the date 2006.
Every available NTP source in Telstra's mobile core came to agree on 2006, an audit found, and some users could not make calls, including emergency calls.
That was a firmware bug. However, the stark reality is that it doesn't take a bug to reproduce the issue: GPS spoofing does the same thing on purpose.
In this blog, we explain how time errors propagate from time servers, why it's dangerous and what can stop an attack.
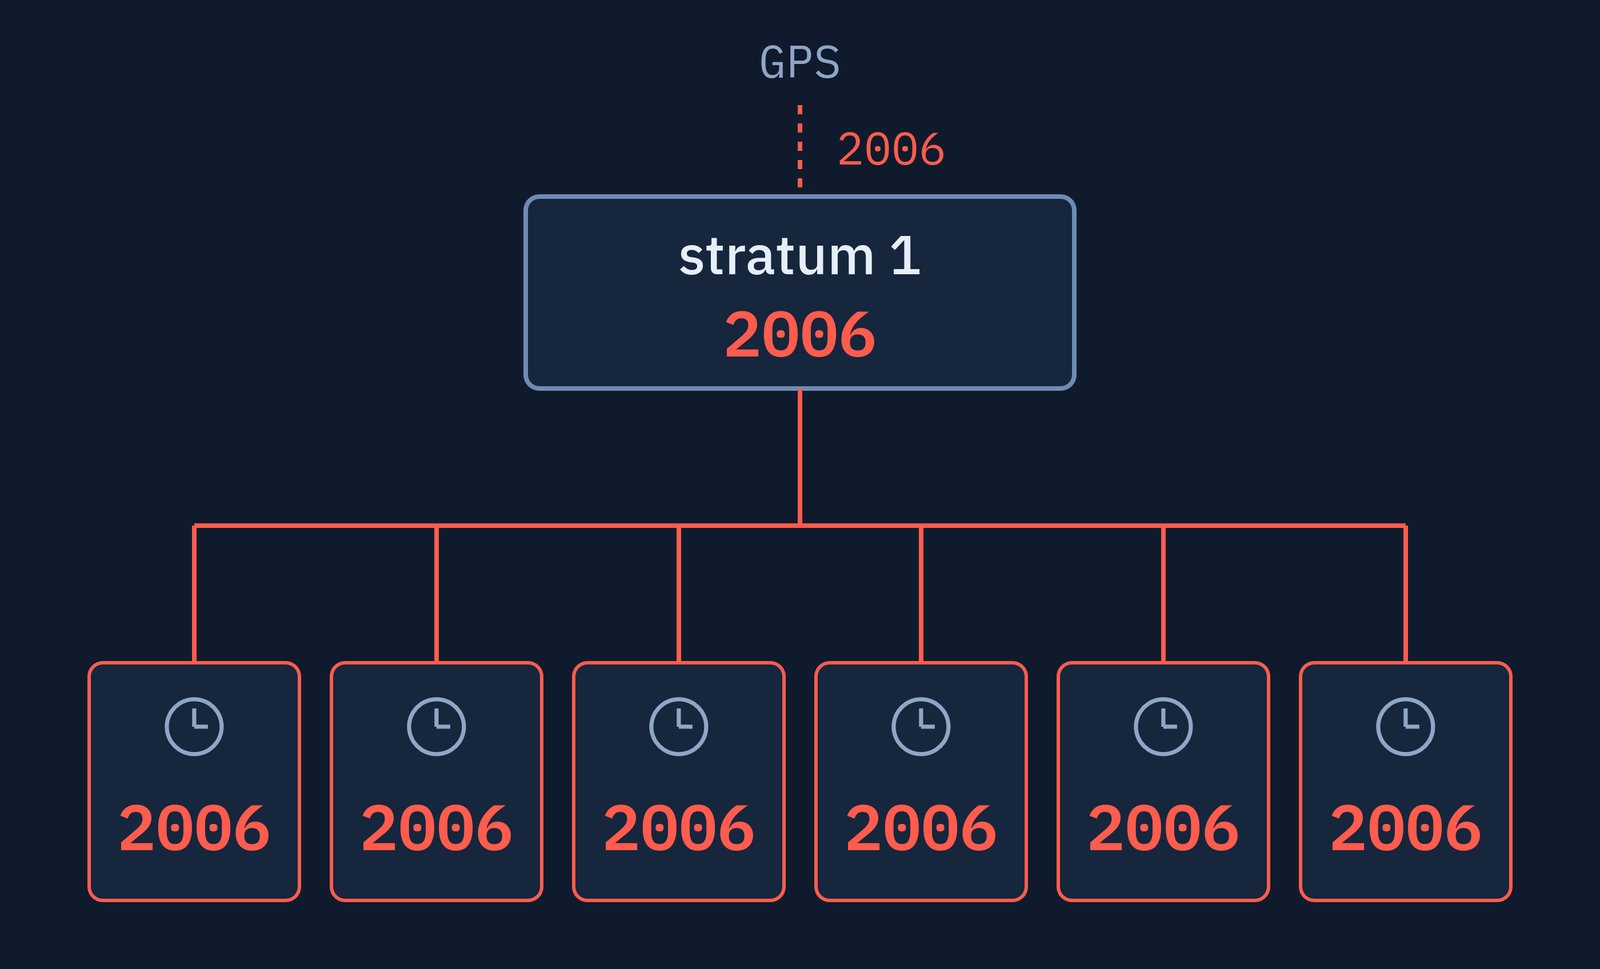
Civil GPS signal carries no authentication.
Europe's Galileo has offered a signed civil signal as an operational service since July 2025, and GPS is still at the requirements stage.
In 2016, Qihoo360 researchers forged GPS and JJY time signals with low-cost parts and moved the clock of their own NTP server, 1,000 seconds at a time. Our NTP post covers what a moved clock breaks.
GPS Spoofing Protections
- The time server can check GPS against its own oscillator. The Meinberg algorithm alarms on unexpected time steps and slow ramps and switches to holdover, using a rubidium oscillator.
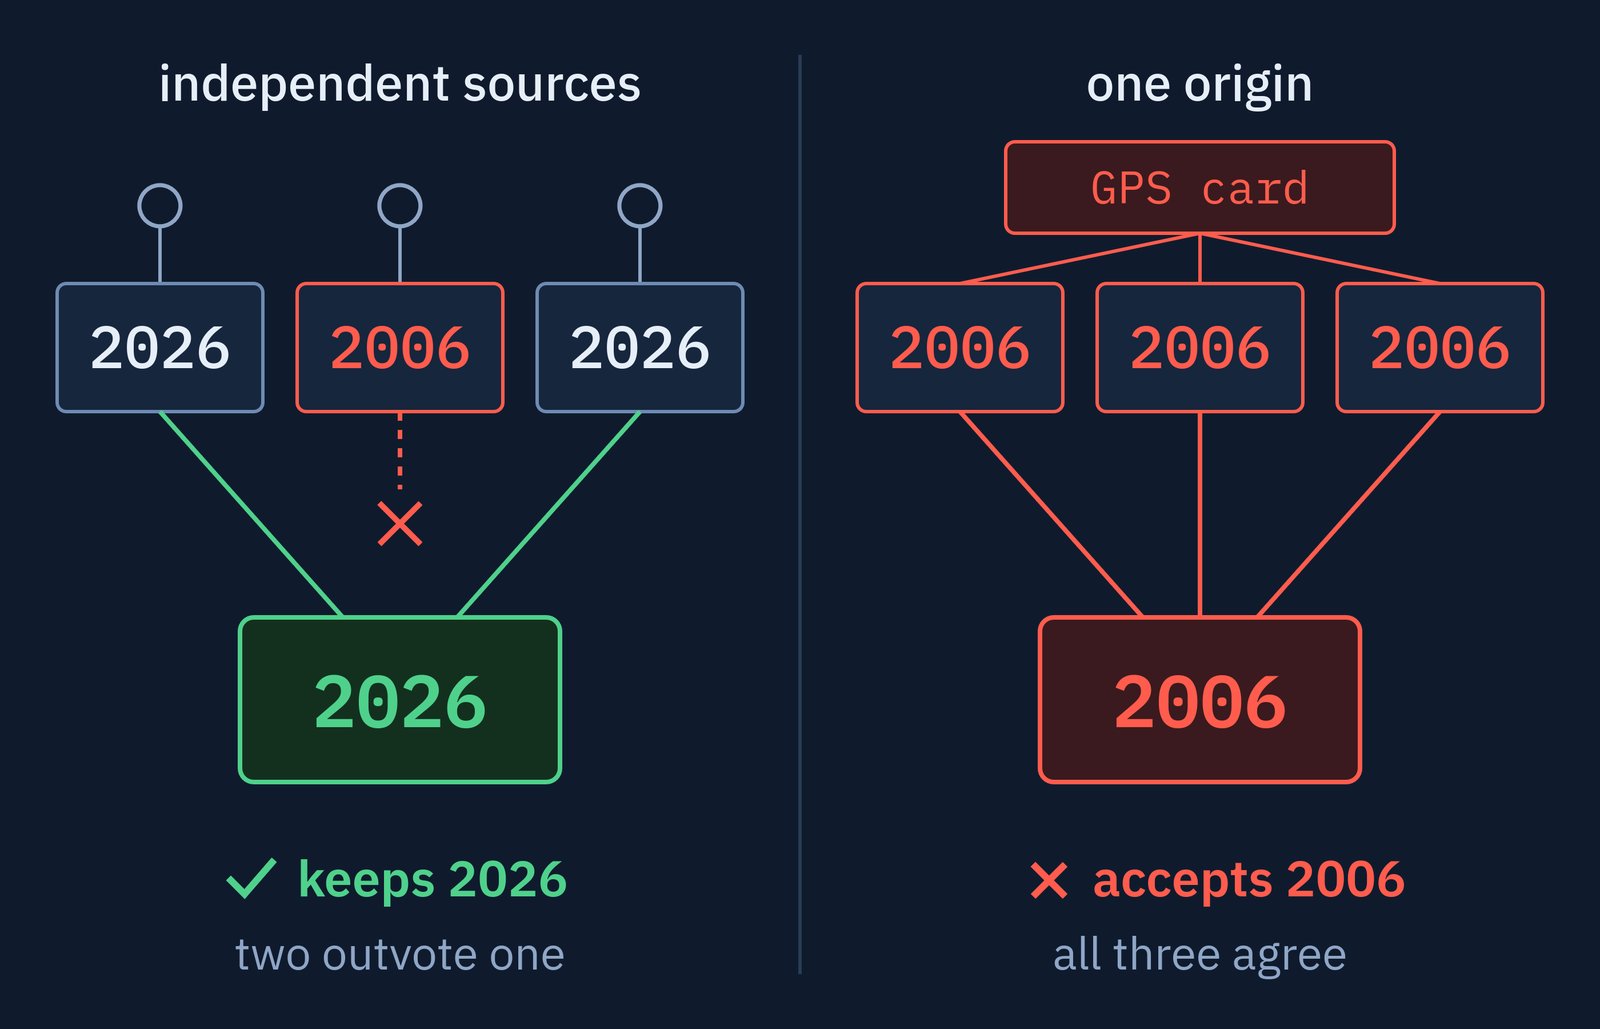
- Clients can outvote one wrong server. This NTP "majority vote" needs independent sources.
Telstra's sources all traced back to one GPS card through peering loops. That's why the bug won the majority vote on the time being 2006.
How to Check Your Time Source
Run timedatectl timesync-status on Linux (chronyc tracking if the machine
runs chrony) or w32tm /query /status on Windows to see the stratum and
reference of what you sync to.
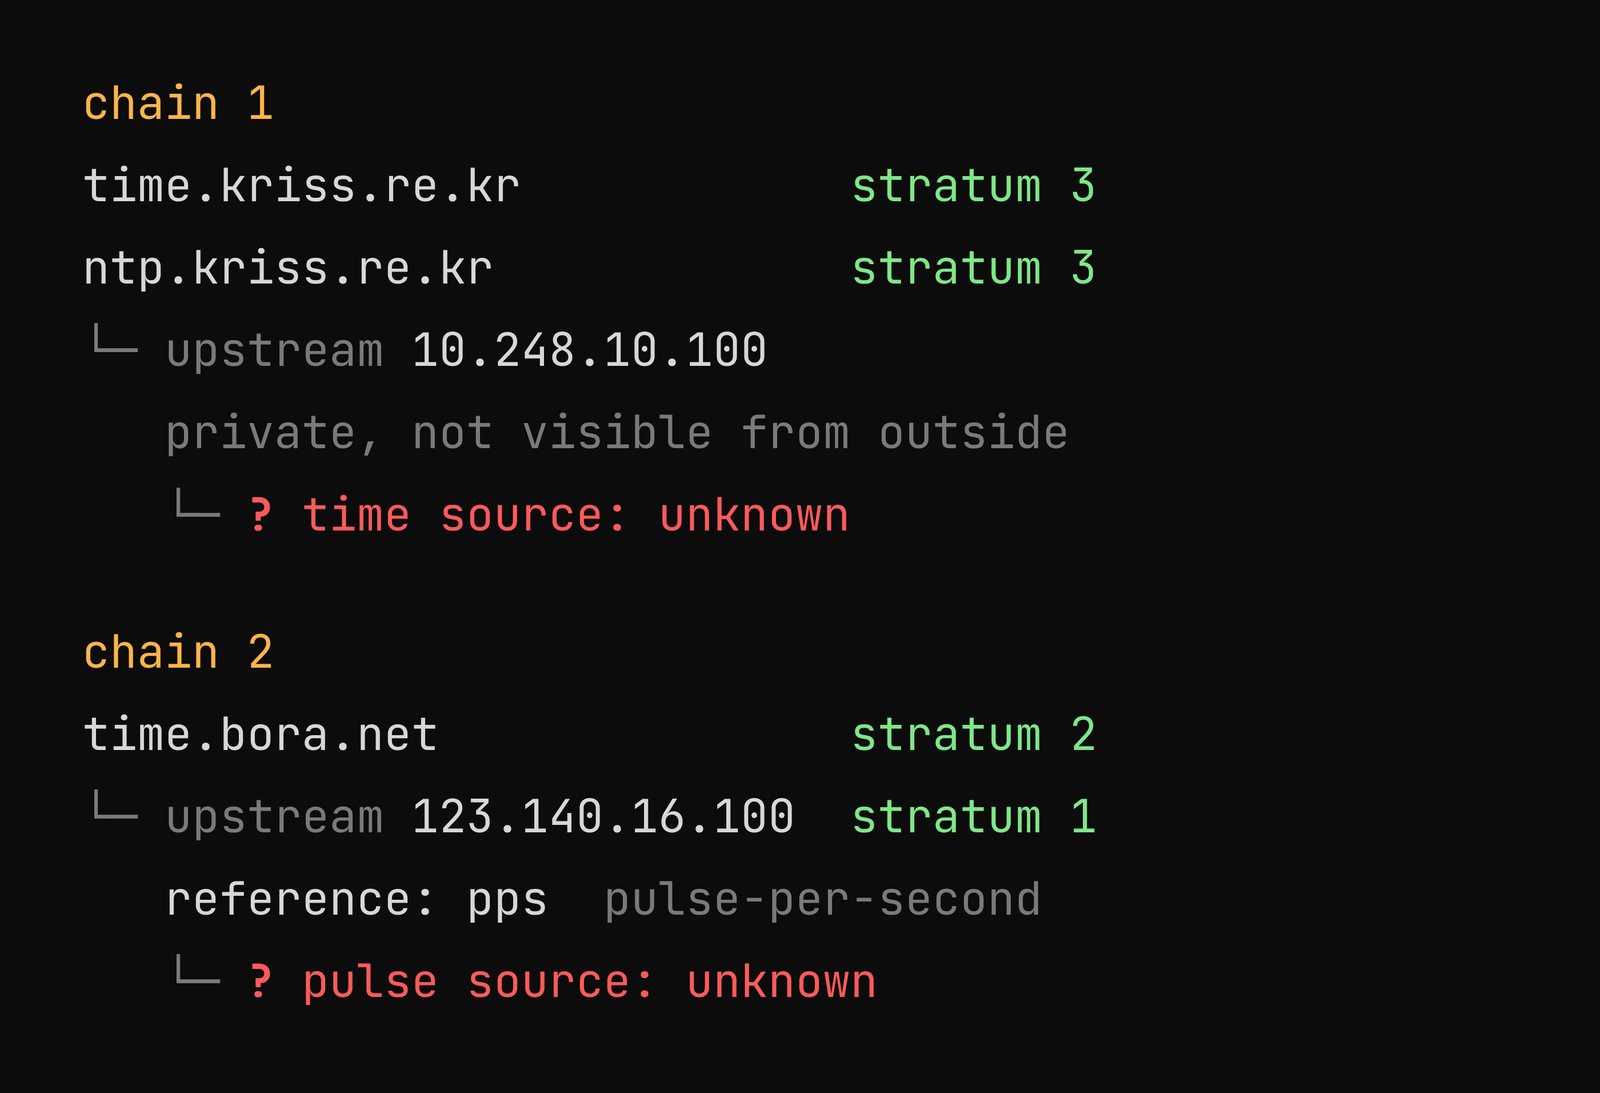
On 3 October 2026, we queried Korea's public NTP servers from inside Korea. Here are the results.
The KRISS (Korea Research Institute of Standards and Science) servers
time.kriss.re.kr and ntp.kriss.re.kr returned stratum 3 with a
private-address refid, so their upstream is hidden.
LG U+'s time.bora.net returned stratum 2. Its upstream returned stratum 1 with
refid pps, a pulse-per-second reference that does not name its source.
References
- Technology Audit Partners — Findings Report on the July 8th Telstra Outage (24 August 2026)
- EUSPA — From Testing to Operations: Galileo OSNMA Service Now Available to Users (5 September 2025)
- Hansen and Skalski (DOT) — DOT Liaisons to the GPS Enterprise (21 April 2026)
- SecurityWeek — NTP Servers Exposed to Long-Distance Wireless Attacks (28 May 2016)
- Meinberg — GNSS Spoofing and How to Mitigate It (14 April 2020)
- Meinberg — Messing with your Radio Time Signal (28 June 2016)

 Instagram